CI/CD Threat Models and Web App Security on AWS: Pipelines, XSS, CSRF, and SQL Injection
Quick summary: GitHub Actions OIDC role sessions are short-lived by design, yet teams still paste static access keys into workflow logs until scanners or audits catch the diff. Supply-chain writeups keep repeating the pattern into 2026.
Key Takeaways
- Supply-chain writeups keep repeating the pattern into 2026
- On May 8, 2026, the dominant CI/CD compromise class is still “credential sprawl meets YAML
- The fix AWS partners recommend, OIDC federation from GitHub Actions to IAM without long-lived keys, is documented end-to-end in our flagship GitHub Actions secure CI/CD guide
- It gives the threat model and maps OWASP-style failures (XSS, CSRF, SQLi) to AWS controls
- Our take: If production deploy still requires an IAM user access key, file a P0 debt ticket
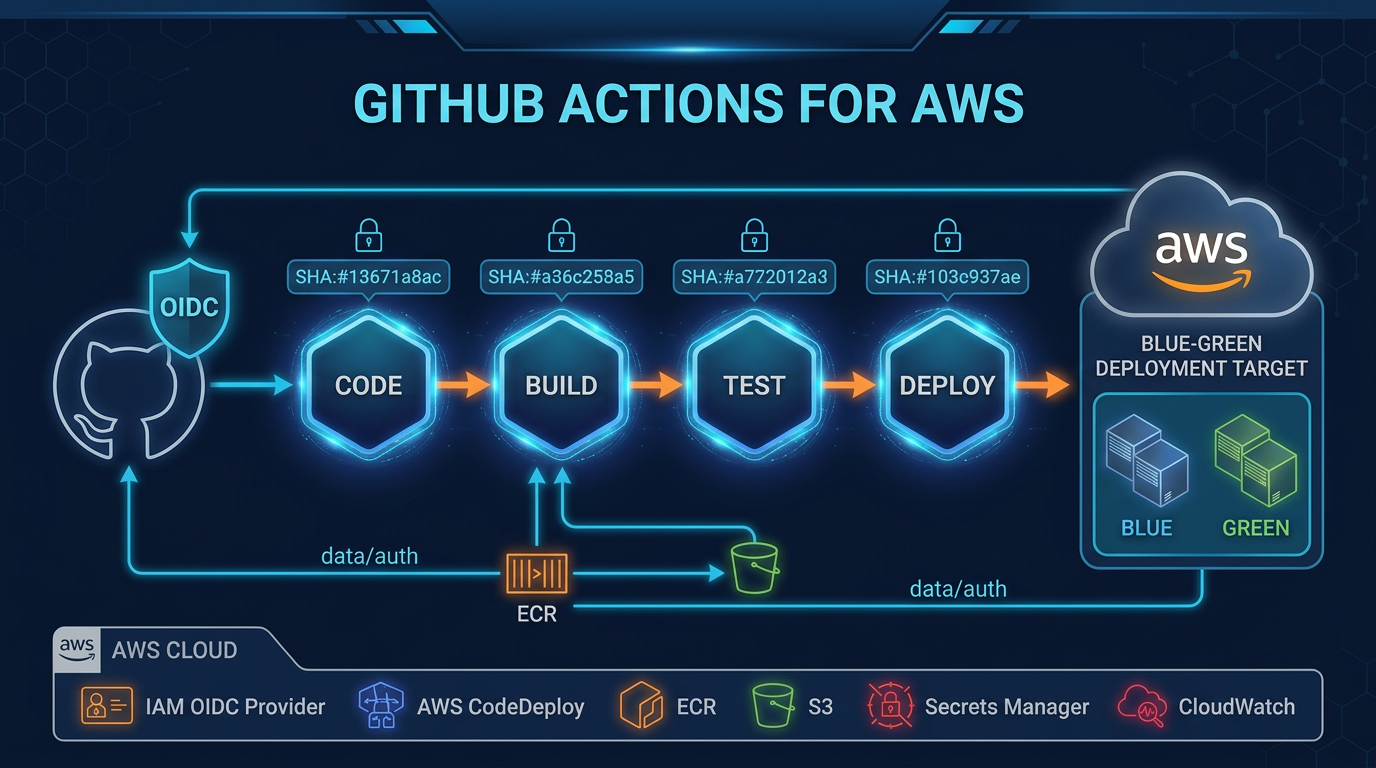
Table of Contents
On May 8, 2026, the dominant CI/CD compromise class is still “credential sprawl meets YAML.” The fix AWS partners recommend, OIDC federation from GitHub Actions to IAM without long-lived keys, is documented end-to-end in our flagship GitHub Actions secure CI/CD guide. This article does not duplicate that playbook. It gives the threat model and maps OWASP-style failures (XSS, CSRF, SQLi) to AWS controls.
CI/CD threat surface
| Threat | Typical failure | AWS-aligned control |
|---|---|---|
| Stolen build secrets | Keys in logs, world-writable buckets | OIDC roles, KMS CMKs, deny policies on public artifacts |
| Malicious PR | Untrusted pull_request_target | Branch protections, CODEOWNERS, ephemeral runners |
| Compromised third-party action | Tag drift / supply chain | SHA pinning, private mirrors |
| Drift between prod/staging | Config-only “hotfix” | Same IaC modules, promotion gates |
Deep procedures: follow the long-form GitHub Actions article; operational checklist lives in the worksheet above.
XSS: layered defenses
Encoding output beats fancy WAF regexes. For internet-facing HTTP, pair code review with AWS WAF production guidance and API abuse protections.
Failure mode: admin consoles trusting rich text stored in RDS without sanitization. WAF cannot see server-side stored XSS rendering inside authenticated sessions.
CSRF: follow your session model
Cookie sessions need CSRF tokens / SameSite discipline. Bearer tokens in memory change the risk posture but widen the XSS blast radius, so pick deliberately.
SQL injection: RDS does not protect you
Use parameterized queries everywhere raw SQL appears. For ORM users: ban string-built WHERE clauses.
Pair database hygiene with broader hardening in 10 AWS security practices and beyond-the-basics workload security.
Full-repository review (May 2026)
PR-time SAST in GitHub Actions security patterns catches diff-sized issues. AWS Security Agent full-repository code review runs broader trust-boundary and data-flow reasoning across the whole tree, which helps with systemic SQLi/XSS paths that never touch a single hot file in one PR.
What this post does not cover
- Container image signing deep dive (refer to Inspector + CI guide cross-links in the GitHub Actions article).
- IAM Permission Boundaries math for deployment roles are covered better in IAM best practices.
If you only do one thing
Turn on organization-level OIDC patterns and delete the last AWS_ACCESS_KEY_ID secret used for deployment. Measure blast radius reduction in quarterly access reviews.
What to do this week
- Walk the pipeline worksheet with security + platform leads; assign owners per unchecked row.
- Run SAST + dependency scan on default branch; block promotion on criticals without risk acceptance record.
- Spot-check top 10 dynamic SQL calls for interpolation, since ORMs hide surprises.
Continue architecture resilience reading at production resilience patterns and data coupling at distributed data field notes.
Frequently asked questions
When is scanning alone insufficient for CI/CD security?
Does AWS WAF replace secure coding for XSS?
How do we stop CSRF for cookie-authenticated APIs?
When does parameterized querying still fail against SQL injection?
Should secrets live in GitHub Actions encrypted secrets forever?
Agentic AI & Cloud Security
Works on making teams more productive with agentic AI. Writes the FactualMinds guides on AWS security and compliance: identity, threat detection, data protection, and audit readiness, the controls AI agents need before they touch production systems.